Switch 2 security cracked, game dumping now possible
A limited jailbreak that began with a delisted app has grown into new exploits that can pull firmware and games off the console and onto a PC.
 Merhabyte Newsdesk · · 2 min read
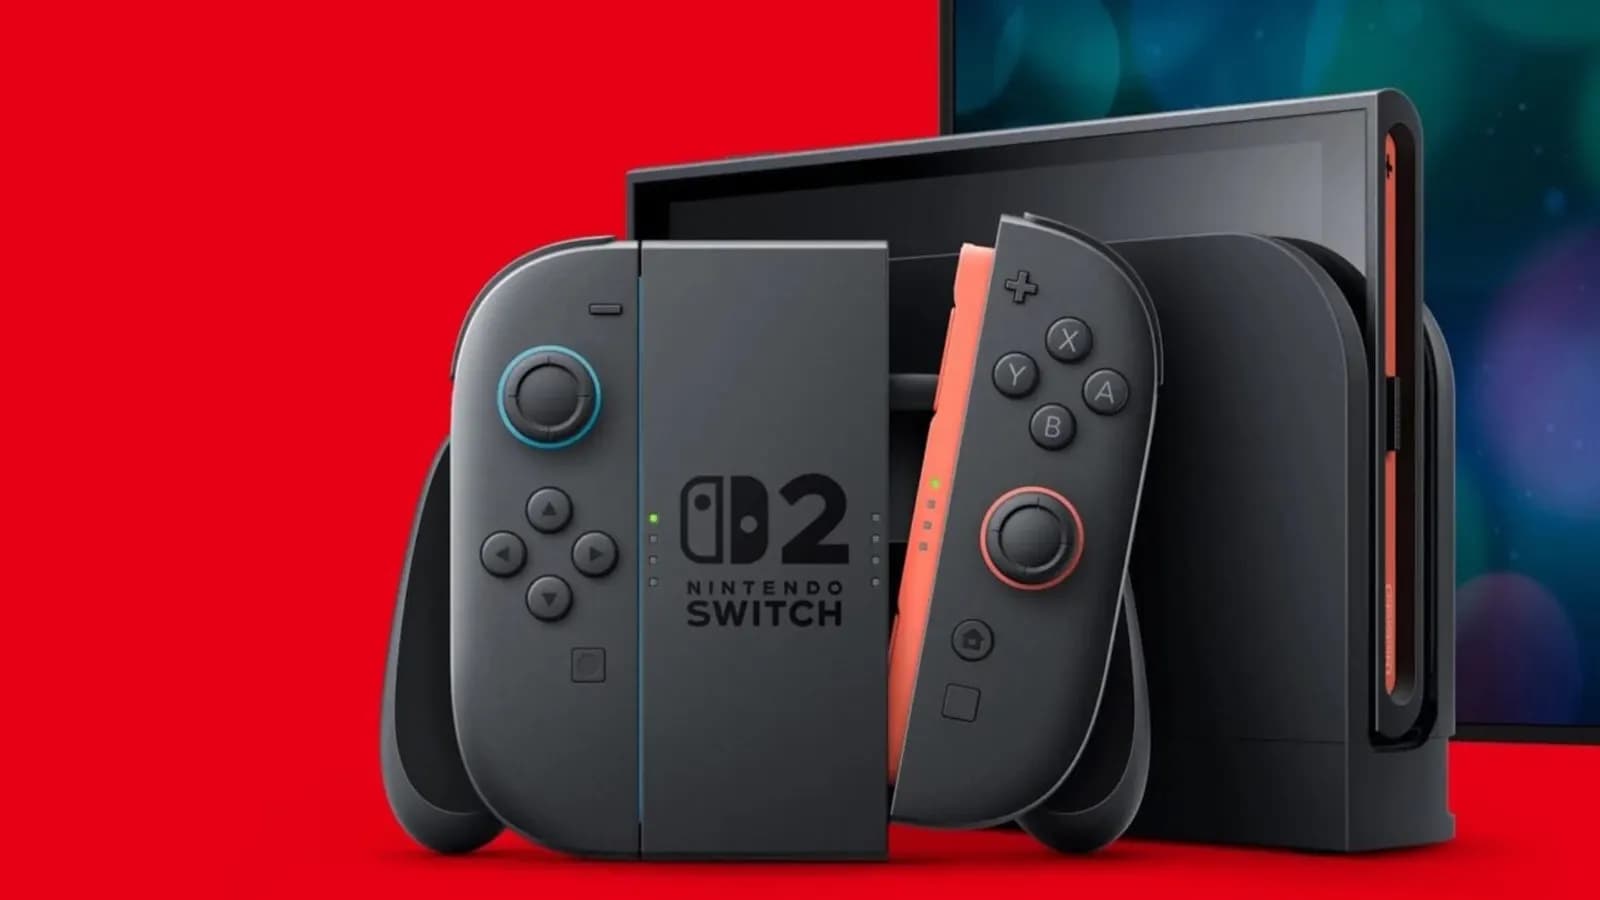
The first jailbreak for the Nintendo Switch 2 surfaced not long ago. Found with the help of generative AI models, it ran through a copy of SmileBASIC, an app since removed from the Switch eShop, and its usefulness was fairly limited. Now hackers have found new exploits that cut far deeper into the console's security.
According to available information, the new exploits break out of the boundaries SmileBASIC imposed. They reportedly open the way to dumping the console's entire firmware to a PC for backup, and to dumping games directly.
From a limited exploit to deeper access
The original jailbreak, which worked through SmileBASIC, let users mod games, install homebrew software, and download and back up save files. Being able to install homebrew also raised the prospect of running pirated games later on. Even so, the discovery fell well short of fully breaking the console's security.
According to information shared on forums and attributed to hardware hacker hexkyz, the new method relies on access to the console's file system. By overloading the file system and memory, the approach appears to have removed the obstacle facing a community that already knew file system access was possible but had been unable to turn it into a usable exploit.
The AI role and access below KIP level
Reportedly, hackers used large language models to discover a specific sequence of operations that causes the console to read certain regions of memory. That in turn gave access to the processes running the console. The exploit is said to allow access to any binary below KIP level, which makes it possible to dump games and applications straight to a PC and extract in-game files.
The exploit has a limitation: with current methods, attacks can only be carried out from within another application, and they must be re-triggered after the console is powered off. On the other hand, now that the flaw and the steps to trigger it are known, it could potentially be triggered through apps other than SmileBASIC. Some hackers are also investigating whether the exploit can be run without needing any particular game or app at all.
Emulation, piracy and Nintendo's response
Full game dumps and closer study of how the console works open the door to emulation, pirate distribution and reverse engineering of Switch 2 games. The original Nintendo Switch was exploited in a similar way early in its life, which helped a broad emulation scene develop over the console's lifespan. Nintendo was thought to have prevented that on the new system.
Nintendo will very likely patch these exploits quickly. Even so, the discovery is a strong first step toward getting past the company's security measures. Factor in the contribution of AI systems to this kind of work, along with warnings from senior executives at AI companies that protecting software against hacking attempts may soon become impossible, and the real question is how long Nintendo can keep hackers out, and whether a complete break of the Switch 2's security is only a matter of time.
Comments
No comments yet. Be the first to comment.