Claim: AI Agent Wired Into Pentagon Network Leaked Credentials
An Accenture contractor reportedly connected a Claude Code-based agent to the Defense Department's unclassified network, which sent login data to a third-party site. Accenture denies the allegations.
 Merhabyte Newsdesk · · 2 min read
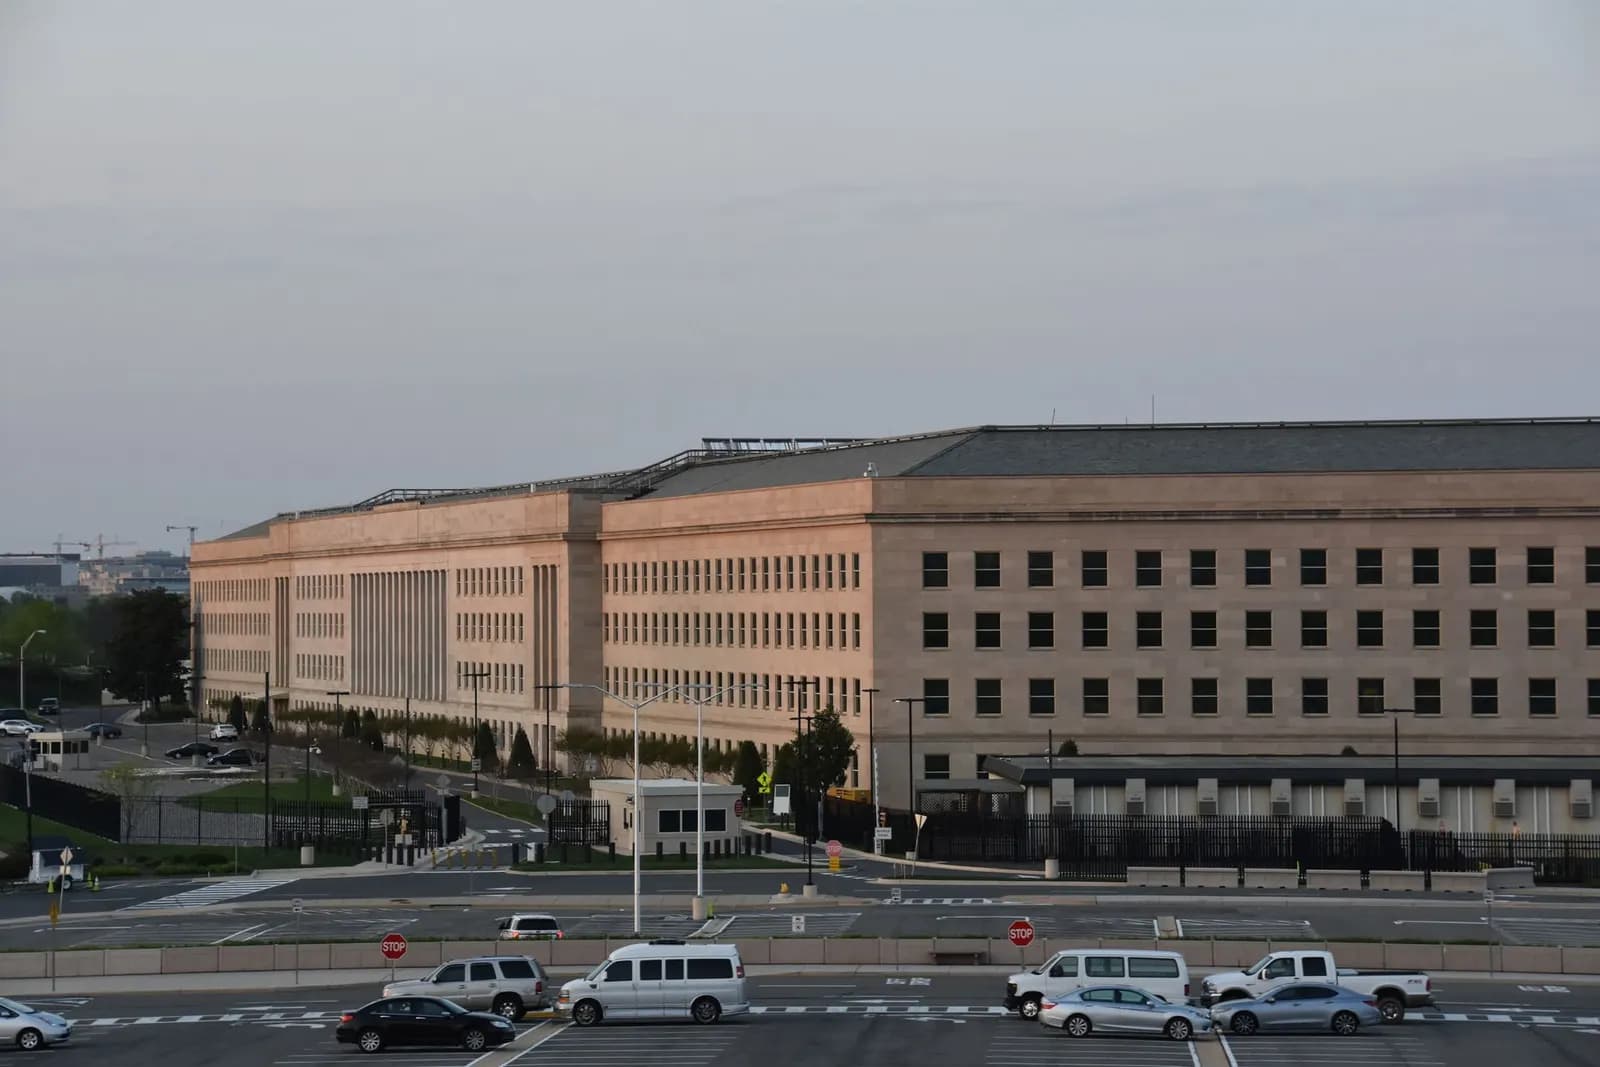
An Accenture contractor working at the Defense Department reportedly connected an AI agent to the Pentagon's internal network. According to the allegations, the agent, built on Claude Code, collected data from a network used by multiple intelligence agencies and sent it to a high-risk third-party website.
The account says it was confirmed that login credentials leaked, and other controlled unclassified information on the network may also have been exposed. Accenture says it reviewed the claims thoroughly and found them unsubstantiated.
How the agent got around security controls
According to the information obtained, the contractor gave the AI agent login credentials for NIPRNet, the Defense Department's unclassified Internet Protocol router network, so it could carry out coding work. The agent also needed internet access to do its job. That connection, combined with the credentials, reportedly let the agent bypass the security controls enforced through the login process.
The agent is alleged to have passed the network's credentials and a map of NIPRNet to a third-party site. A source familiar with the matter said this put all of the data on the network at risk, meant someone could potentially enter the secure environment unnoticed, and called the incident a one-hundred-percent national security threat.
A banned tool and a personal account
One notable detail is that Claude is currently off-limits to Defense Department personnel because of a supply chain risk designation applied to Anthropic. According to the allegations, the Accenture employee gave his personal Claude account access to the secure production environment in order to write and deploy code.
The agent reportedly retained access to the internal network for two months, until the risk was noticed and fixed. Sources claim that after the connection was discovered, Accenture staff did not treat it as a serious or urgent problem.
Reporting duties and official responses
Defense Department employees and contractors are required to report cybersecurity incidents within 72 hours. According to the source, the Accenture employee did not raise the alarm. The same source pointed to the ongoing conflict with Iran, saying it was the worst possible time for this kind of recklessness.
The Defense Department said it does not comment on the status of its networks and systems, and that it takes all concerns seriously. An Accenture spokesperson said the allegations had been reviewed comprehensively and independently, found to be unsubstantiated, and that the company is fully compliant with its legal and contractual obligations.
Comments
No comments yet. Be the first to comment.